The AI Act at Work: Annex III Point 4, Prohibited Practices and the Deployer's Duties
Part V asks what European law already says about the allocation of decision rights that Chapter 20 set out, starting with the instrument that names work most directly. Regulation (EU) 2024/1689, the AI Act, classifies AI used in employment and workers' management as high-risk, prohibits one practice at the workplace outright, places duties on the employer that deploys a high-risk system and gives the people affected a right to an explanation (1, European Union, 2024). Regulation (EU) 2026/1744, the Digital Omnibus on AI, has since changed when most of those duties apply and how AI literacy is framed, while leaving the employment provisions themselves in place (2, European Union, 2026). This chapter reads those provisions as organisational and architectural implications, not as legal advice. It concerns M1 Direction, because the Act lists the allocation of tasks; M2 Evaluation, because it lists the monitoring and evaluation of performance and behaviour and prohibits emotion recognition at work; M3 Consequence, because it lists recruitment, promotion, termination and decisions affecting the terms of work; and M5 Care, because the duty to inform workers and their representatives, and the prohibition itself, protect voice, health and dignity.
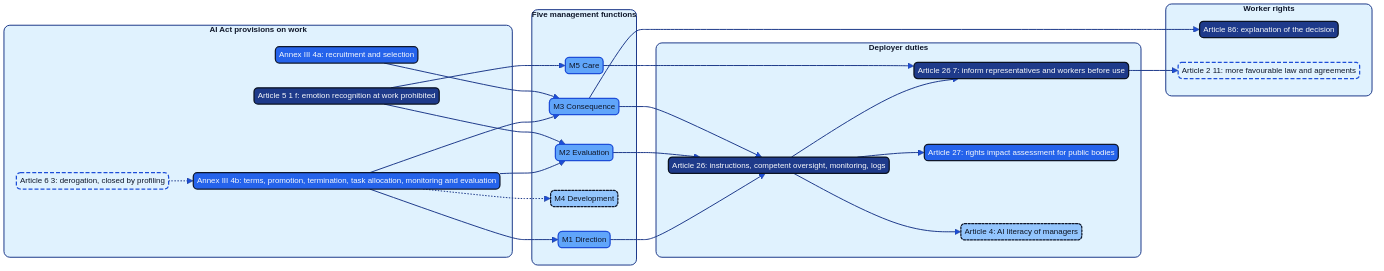
Figure 21.1: The AI Act's provisions on work mapped onto the five management functions, with the high-risk listing, the prohibition, the deployer's duties and the worker's rights.
Employment in the AI Act
The AI Act regulates by risk and by role. A provider develops an AI system and places it on the market or puts it into service under its own name; a deployer uses it under its authority (Article 3). An employer that buys a rostering system is a deployer; an employer that builds its own allocation agent is provider and deployer at once. Annex III lists the uses that make a system high-risk, and its point 4 is headed "Employment, workers' management and access to self-employment".
Recital 57 gives the reason: such systems "may have an appreciable impact on future career prospects, livelihoods of those persons and workers' rights"; they may perpetuate historical patterns of discrimination against women, age groups, persons with disabilities or persons of certain racial or ethnic origins or sexual orientation; and monitoring systems may undermine the rights to data protection and privacy (1, European Union, 2024). The recital includes persons providing services through platforms, so the Act reaches beyond the employment contract to what this book calls workers.
Against the five management functions of Chapter 2, recruitment, terms, promotion and termination are M3 Consequence, task allocation is M1 Direction, and monitoring and evaluation is M2 Evaluation. M4 Development appears only indirectly: the Commission's draft guidelines on classification treat training as falling within point 4(b) where completing or passing it is a condition of promotion, pay or keeping the job (3, European Commission, 2026). M5 Care is not listed as a use, but it is the function the Act's other employment provisions protect: the prohibition of emotion recognition, the duty to inform workers before a system is used, and the explicit statement in Article 2(11) that the Act does not preclude laws or collective agreements more favourable to workers.
Two features shape what follows. Classification follows the intended purpose, not the technology or the vendor's label, so one system can serve two purposes and be classified differently for each. And the Act sits on top of labour and data protection law: recital 92 says it is without prejudice to employers' duties to inform and consult workers, naming Directive 2002/14/EC (51, European Union, 2002). The GDPR (Chapter 22), co-determination (Chapter 23) and occupational safety and equality law (Chapter 24) remain where they were.
Annex III point 4
Point 4(a) covers "AI systems intended to be used for the recruitment or selection of natural persons, in particular to place targeted job advertisements, to analyse and filter job applications, and to evaluate candidates". Point 4(b) covers "AI systems intended to be used to make decisions affecting terms of work-related relationships, the promotion or termination of work-related contractual relationships, to allocate tasks based on individual behaviour or personal traits or characteristics or to monitor and evaluate the performance and behaviour of persons in such relationships" (1, European Union, 2024). Chapter 7 treats point 4(a); this chapter concentrates on point 4(b), whose four limbs map onto familiar management practice.
Decisions affecting terms. The Commission's draft guidelines of May 2026, updated in July 2026, read "decisions" functionally: any act or omission attributable to the employer that materially affects the worker's contractual position or the modalities of the work, including cases in which a person formally takes the decision but relies significantly on the system's output (3, European Commission, 2026). Terms include pay, working-time arrangements, leave and rest periods; the draft gives the denial of a leave request and a significant change to regular working hours as examples. Day-to-day adjustments within the existing terms, such as allocating desks, do not qualify. A rostering system that fixes four weeks of working hours sits above that threshold.
Promotion and termination. The draft reads termination to include system-driven non-renewal of a fixed-term contract and the definitive suspension of a platform account, because the effect is the same as dismissal.
Task allocation based on individual behaviour or personal traits. The draft guidelines treat behavioural indicators such as punctuality, responsiveness, reliability metrics, acceptance rates and performance ratings as "personal traits or characteristics", and give as an example a scheduler that ranks workers for each slot by punctuality, no-show history and acceptance rates and gives the best shifts to the highest-ranked. Allocation on objective, neutral and external criteria tied to the job, such as availability declared by the worker, a required licence or geographical proximity, falls outside the limb. The dividing line runs through the optimiser's feature list.
Monitoring and evaluation of performance and behaviour. The draft treats this as an autonomous category, covering systematic monitoring or evaluation whether or not it changes a formal term. Output counts and ratings that feed employee files are in; systems used only for external legal obligations, purely for safety, or that flag issues to the worker alone are out.
The guidelines are a draft and the Commission's interpretation, not the law; the Court of Justice has the last word. They are nevertheless the most concrete working reading available, and they draw the lines this book draws between functions. Allocation by availability and competence is M1 Direction that the Act leaves alone; allocation by behaviour is M1 Direction that has become M2 Evaluation by another name, and the Act treats it as such.
The Article 6(3) derogation
Article 6(3) lets a provider conclude that a system listed in Annex III is not high-risk because it "does not pose a significant risk of harm to the health, safety or fundamental rights of natural persons, including by not materially influencing the outcome of decision making". One of four conditions must be met: the system performs a narrow procedural task; it improves the result of a previously completed human activity; it detects decision-making patterns or deviations from them without replacing or influencing the human assessment without proper review; or it performs a preparatory task to an assessment (1, European Union, 2024). Recital 53 gives examples such as classifying incoming documents, detecting duplicate applications and translation.
The derogation is then closed by one sentence: a system listed in Annex III "shall always be considered to be high-risk where the AI system performs profiling of natural persons". Article 3(52) takes the definition of profiling from Article 4(4) of the GDPR (5, European Union, 2016), and the draft classification guidelines restate it as automated processing of personal data to evaluate personal aspects of a person, naming performance at work, reliability and behaviour among them (3, European Commission, 2026). A management system that evaluates individual workers is profiling by definition. The derogation therefore helps only at the edges: a tool that collates timesheets into a report without scoring or flagging anyone, which the draft gives as a preparatory task, or one that reminds a manager that a fixed-term contract is about to lapse. It does not help a system whose value lies in comparing people.
A provider that relies on the derogation must document its assessment beforehand and register the system under Article 49(2) (Article 6(4)); the Omnibus streamlined that registration but kept it (2, European Union, 2026). The conclusion is made for the purpose the provider states: a deployer that uses a "not high-risk" product to rank workers changes the intended purpose and, under Article 25(1)(c), is treated as its provider. The vendor's classification is evidence to check, not a conclusion to adopt, which is the reason AI Governance, Chapter 8 makes classification a versioned record re-opened by change (41, Nordqvist, 2026). This chapter builds on that conclusion (F16).
Prohibited at work
Article 5(1)(f) prohibits "the placing on the market, the putting into service for this specific purpose, or the use of AI systems to infer emotions of a natural person in the areas of workplace and education institutions, except where the use of the AI system is intended to be put in place or into the market for medical or safety reasons" (1, European Union, 2024). Recital 44 cites the weak scientific basis of emotion inference and the imbalance of power at work. The prohibition has applied since 2 February 2025, and infringements of Article 5 carry the Act's highest fines, up to EUR 35 million or 7 per cent of worldwide annual turnover (Article 99(3)).
The Commission's guidelines on prohibited practices, whose content was approved in February 2025 and which were formally adopted in July 2025, set out how the Commission reads the prohibition (58, European Commission, 2025). Five points matter for an employer.
First, scope follows the definition of an emotion recognition system in Article 3(39): emotions or intentions inferred from biometric data. Inferring sentiment from written text is outside the prohibition; inferring emotion from voice, facial expression, posture, movement or keystroke dynamics is inside it. Second, "emotion" is read widely, and relabelling an emotion as an "attitude" does not escape the prohibition; physical states such as pain or fatigue are not emotions, so a system that detects a driver's fatigue to prevent an accident is not emotion recognition at all. Third, "workplace" is read broadly: any physical or virtual space where people perform tasks assigned by their employer or the organisation they work with, whatever their status, including candidates in recruitment and the probationary period. Prohibited examples include a call centre tracking its employees' anger, emotional-tone monitoring of hybrid meetings and emotion recognition in recruitment; tracking customers' emotions to help an employee handle a call is not prohibited. Fourth, the medical and safety exception is narrow: wellbeing, stress and burnout monitoring are not medical reasons, safety means life and health, and stress detection is allowed only where stress itself poses a specific danger, with no reuse of the data to assess performance. Fifth, emotion recognition used only for an individual's own training is allowed if the results are not shared with HR and cannot affect the person's assessment or promotion.
Article 5(1)(g) adds a second prohibition that touches work: biometric categorisation to deduce or infer, among other things, trade union membership. And the prohibition does not stand alone. Annex III point 1(c) makes emotion recognition outside the prohibited areas high-risk, and the draft classification guidelines state that where a system falls within both a prohibition and point 4, the prohibition prevails (3, European Commission, 2026).
For the architect, the implication is a list of features that must be switched off, with evidence that they are: interview scores for "confidence" or "engagement" derived from video or voice, agent-emotion analytics in contact-centre suites, mood inference from meeting audio, stress estimates from typing patterns or wearables. A hidden setting is not enough. The contract states that the feature is disabled for the tenant, the deployer tests that no inferred-emotion field appears in exports, logs or APIs, and the check is repeated after every release, because Mode 0 features arrive with licence updates rather than procurement decisions.
The deployer's duties
The obligations on providers of high-risk systems sit in Articles 9 to 15 and 16 to 25: a risk management system (Article 9), data governance with bias examination (Article 10, now complemented by the Omnibus's Article 4a on processing special categories of data for bias detection), technical documentation (Article 11), automatic logging (Article 12), transparency and instructions for use (Article 13), design for human oversight (Article 14), and accuracy, robustness and cybersecurity (Article 15) (1, European Union, 2024) (2, European Union, 2026). For the systems in point 4, conformity is assessed by internal control under Annex VI, without a notified body (Article 43(2)). Article 14(4) describes what the deployer's overseers must be able to do: understand the system's limitations, remain aware of automation bias, interpret the output, override it and stop the system safely. The employer cannot meet its own duties unless the provider has built these capabilities, so they belong in the tender.
Article 26 sets out the deployer's duties. An employer that uses a high-risk management system must use it according to the instructions for use (Article 26(1)); assign human oversight to natural persons "who have the necessary competence, training and authority, as well as the necessary support" (Article 26(2)); ensure that input data under its control is relevant and representative (Article 26(4)); monitor operation, suspend use and inform the provider and the market surveillance authority where the system presents a risk, and report serious incidents (Article 26(5)); keep the logs under its control for at least six months unless other law, in particular data protection law, provides otherwise (Article 26(6)); inform workers' representatives and affected workers before use (Article 26(7)); as a public authority, register its use and refuse a system the provider has not registered (Article 26(8) and Article 49(3)); use the provider's information in its data protection impact assessment (Article 26(9)); and tell the people about whom the system makes or assists decisions that they are subject to it (Article 26(11)), which recital 93 says should include the intended purpose, the type of decisions and the right to an explanation.
Three of these duties carry the weight in management. Article 26(2) is the legal anchor of this book's named human decider. Competence, training and authority are three separate requirements, and the third is the one employers most often omit: a unit manager who may not depart from a roster without a request to central HR has competence and training but not authority. The Transformed Security Architect, Chapter 18 drew the conclusion that regulation places duties on named people, that someone must turn each article into a control and that accountability cannot be delegated to a system (46, Nordqvist, 2026); this chapter builds on it (F78), and Chapter 26 turns Article 26(2) into an oversight record and an oversight-quality metric.
Article 26(7) is the provision written for workplaces. Employers must inform "workers' representatives and the affected workers that they will be subject to the use of the high-risk AI system" before putting it into service or using it at the workplace, where applicable under the rules and procedures of Union and national law (1, European Union, 2024); recital 92 says it fills gaps and reduces no existing right. Four implications follow. The duty is information, not consultation or co-determination; where national law gives more, as the German Works Constitution Act does through co-determination over technical equipment suited to monitor (9, Germany, 2001) and the Swedish co-determination act does through the duty to negotiate before an important change (205, Sveriges riksdag, 1976), national law governs and Article 2(11) protects it. The duty runs to both representatives and the affected workers individually, so a works-council briefing does not replace a notice to the people rostered by the system. The duty is prior: it falls before use, so a pilot at one unit triggers it for that unit. And because the text only requires workers to be told that they will be subject to the system, the content of a useful notice (what the system does, which function it performs, at what degree of delegation, who decides, how to contest) is left to the employer; Chapter 28 designs the worker information notice that meets it.
Article 26(5) and (6) let financial institutions meet the monitoring and log-keeping duties through their internal-governance rules under Union financial services law. For any employer, though, the six-month minimum for logs meets the GDPR's storage limitation, and the retention of logs that record individual workers' activity needs its own justification in the data protection impact assessment.
Impact assessment and explanation
Article 27 requires a fundamental rights impact assessment before a high-risk Annex III system is first deployed by bodies governed by public law, by private entities providing public services and by deployers of the credit and life and health insurance systems in points 5(b) and (c) (1, European Union, 2024). A regional authority rostering its own staff must therefore assess; a private insurer allocating work to its claims handlers need not, because its point 5(c) duty attaches to underwriting. The assessment covers the processes, period and frequency of use, the persons affected, the specific risks of harm, the oversight measures and the measures if risks materialise, including complaint mechanisms. The deployer notifies the market surveillance authority of the result and updates the assessment when an element changes.
The Omnibus amended two paragraphs. Where the data protection impact assessment already covers an element, the deployer may cross-refer to or include the relevant sections of it, and the AI Office's template questionnaire, which may be an automated tool, is to give that option (2, European Union, 2026). This helps, provided the two assessments still ask different questions: the DPIA about personal data, the rights assessment about working conditions, equal treatment, dignity and health, which the Charter protects in Articles 31, 21 and 8 among others (48, European Union, 2012). Recital 96 suggests involving representatives of affected groups; for a workforce, those are the unions and safety representatives.
Article 86 gives "any affected person subject to a decision which is taken by the deployer on the basis of the output from a high-risk AI system listed in Annex III" that produces legal effects or similarly significant effects which the person considers adverse to their health, safety or fundamental rights the right to obtain "clear and meaningful explanations of the role of the AI system in the decision-making procedure and the main elements of the decision taken" (1, European Union, 2024). Three features make it a design requirement. The right runs to the employer, not the vendor. The trigger is the person's own view of adverse impact, so the employer cannot filter requests by its view of their merit. And the explanation covers both the system's role and the main elements of the decision. An employer that can say which version of the roster optimiser proposed the schedule, which constraints applied, what the manager changed and why, can answer; an employer that only kept the final roster cannot. That is the Management Decision Record of Chapter 25, and Chapter 27 builds the appeal path on it. Article 86(3) limits the right to cases where Union law does not already provide it; its relationship to the GDPR and the Platform Work Directive (47, European Union, 2024) is left to Chapter 22.
AI literacy for managers
Article 4 applied from 2 February 2025 and was rewritten by the Omnibus. Providers and deployers "shall take measures to support the development of AI literacy of their staff and other persons dealing with the operation and use of AI systems on their behalf", taking into account their knowledge, experience, education and training, the context of use and the persons on whom the systems are used; the obligation "does not require providers or deployers to guarantee any specific level of AI literacy of any individual" (2, European Union, 2026). The Commission's questions and answers, updated in October 2026, state that AI literacy remains an obligation, that no "sufficient" level is mandated, that there is no obligation to measure employees' knowledge, and that for deployers of high-risk systems the obligation to train staff for human oversight remains in place (4, European Commission, 2026).
The softening changes less than it seems, because a manager who oversees a high-risk management system is covered by Article 26(2), which was not amended. AI Governance, Chapter 14 concluded that AI literacy is role-specific and must be evidenced in a competence framework and in individual records (41, Nordqvist, 2026); this chapter builds on that conclusion (F25). For a line manager who approves rosters or reassigns work proposed by an agent, the content is concrete: what the system optimises and cannot see, which inputs are behavioural, how automation bias shows itself in one's own approvals, how to override, record a reason and escalate, and how to answer a request for an explanation. Training the workers' representatives and safety representatives who receive the system's outputs is not required in so many words, but it is the cheapest way to make the information given under Article 26(7) intelligible.
Dates and the Digital Omnibus
Under Article 113 as amended by Regulation (EU) 2026/1744, in force since 27 July 2026, the dates are as follows (1, European Union, 2024) (2, European Union, 2026).
| Provision | Applies from | Status for an employer |
|---|---|---|
| Chapters I and II: definitions, Article 4 AI literacy, Article 5 prohibitions including 5(1)(f) | 2 February 2025 (Article 4 in its amended form since 27 July 2026) | Observable law in force |
| Penalties, governance and general-purpose AI model rules (Chapter III Section 4, Chapters V, VII, XII) | 2 August 2025 | Observable law in force |
| General date of application, including Article 86 and Chapter IX | 2 August 2026 | Observable law in force; interplay with the deferred classification rules to be settled |
| Chapter III Sections 1 to 3: classification, provider requirements, Articles 26 and 27, for Annex III systems | 2 December 2027 | Expected: decided date, not yet applicable |
| Chapter III Sections 1 to 3 for Annex I product systems | 2 August 2028 | Expected; rarely relevant to management |
| High-risk systems already in service before the Chapter III date: covered only after significant design changes; public-authority systems in any case by 2 August 2030 (Article 111(2) as amended) | Transitional | Expected; reliance on it needs a recorded decision |
Recital 40 of the Omnibus gives the reason for the deferral: harmonised standards, common specifications and national competent authorities were not ready. The deferral is a planning fact, not an exemption; the prohibition, the literacy obligation, national information and consultation duties and the GDPR apply now. Two questions remain open on the text and are labelled accordingly. Article 86 sits in Chapter IX, whose date the Omnibus did not move, but it refers to systems "listed in Annex III" whose classification rules apply from 2 December 2027; how the two dates will be read together is speculation, and the cautious employer can answer an explanation request today. And Article 111(2) covers a system already in service only once its design changes significantly, a point that a model retrained quarterly reaches quickly. Neither organisation in this book relies on it.
The content of harmonised standards for the requirements in Articles 9 to 15 is expected but not yet settled. Until they are cited, a deployer asks for the provider's evidence against the articles, structured where possible along a management system such as ISO/IEC 42001 (10, ISO/IEC, 2023). Enforcement practice in employment is speculation until supervisors act.
Outside the Union the Act does not apply as law. Norway follows through the EEA Agreement once the Act is incorporated, the United Kingdom and Switzerland have their own regimes, and the Council of Europe's Framework Convention on AI and Human Rights, Democracy and the Rule of Law is a separate treaty open to states beyond the Union, whose effect on employment practice is expected only where states ratify and implement it (59, Council of Europe, 2024).
From articles to controls
The articles become useful when each is a control with an owner, a trigger and evidence, as The Transformed Security Architect, Chapter 18 showed for NIS 2 and DORA (46, Nordqvist, 2026) and AI Governance, Chapter 9 showed for governance as code (41, Nordqvist, 2026). Seven controls cover a management system: classification per function, the prohibition check, named oversight, prior information, the impact assessment, the explanation and monitoring. The excerpt below shows the shape; Chapter 25 places the same entries in the delegation register.
# management/ai-act-controls.yaml (illustrative excerpt)
version: 3
applies_to: high-risk management systems under AI Act Annex III point 4
controls:
  - id: AIA-CLS-01
    article: "Article 6(2), Annex III point 4; Article 6(3)"
    functions: [M1, M2, M3]
    owner: AI governance lead
    trigger: [new system, new intended purpose, model or rule change, regulatory change]
    evidence: classification AIDR per system and per function
  - id: AIA-PRH-01
    article: "Article 5(1)(f), Article 5(1)(g)"
    functions: [M2, M5]
    owner: system owner
    trigger: [procurement, every vendor release]
    evidence: contract clause, configuration export, negative test of exports and APIs
  - id: AIA-OVS-01
    article: "Article 26(2), Article 14(4)"
    functions: [M1, M2, M3]
    owner: line manager of each overseer
    evidence: named overseers, training record, written authority to override
  - id: AIA-INF-01
    article: "Article 26(7), Article 26(11)"
    functions: [M5]
    owner: HR director or entity HR lead
    trigger: before first use in each unit or entity
    evidence: representatives' acknowledgement, worker information notice version
  - id: AIA-FRA-01
    article: "Article 27"
    functions: [M1, M2, M3, M5]
    owner: system owner
    trigger: before first use; on change of any Article 27(1) element
    evidence: FRIA record and notification to the market surveillance authority
  - id: AIA-EXP-01
    article: "Article 86"
    functions: [M3]
    owner: named human decider
    evidence: Management Decision Record per decision
  - id: AIA-MON-01
    article: "Article 26(5), Article 26(6)"
    functions: [M1, M2, M5]
    owner: system owner
    evidence: monitoring plan, suspension criteria, log retention justified in the DPIA
Practical guide: Classifying an AI system that touches management functions under the AI Act, and recording the result
Purpose. Establish, before procurement or build and on every relevant change, whether a system that takes part in managing people is prohibited, high-risk or neither, and record the result so that a works council, a supervisor or a court can follow the reasoning.
Roles. The system owner leads; the AI governance lead and HR prepare the assessment; the data protection officer reviews profiling and the DPIA; a workers' representative is informed and may comment; the line managers who will oversee the system describe how it is actually used. Legal counsel reviews the result.
Steps.
- Describe the system by function, not by product. List each output, the management function it serves, the degree of delegation, who sees it and what decision it feeds. Treat each function as a separate intended purpose.
- Run the prohibition check first. Ask whether any feature infers emotions from the biometric data of workers or candidates, or infers trade union membership or other protected characteristics. If so, switch it off and verify before anything else; claim the medical and safety exception only with a written expert opinion and a specific danger.
- Test each function against Annex III point 4. For recruitment, apply point 4(a). For everything after hiring, test the four limbs of point 4(b): does the output decide or significantly shape a term of work (hours, rest, leave, pay), a promotion or a termination; does it allocate tasks on behavioural inputs (list every input feature and mark each as objective and job-related or behavioural); does it monitor or evaluate individual performance or behaviour, and does anyone other than the worker see the result?
- Test the derogation narrowly. Claim Article 6(3) only if one of its four conditions is met and the function does not evaluate any individual. If the system compares people, record that it performs profiling and that the derogation is unavailable.
- Establish your role. Record whether you are deployer, provider or both, and whether your use changes the intended purpose the provider declared (Article 25(1)(c)). Compare your conclusion with the provider's and record any disagreement.
- Map the consequences. For a high-risk function, list the provider evidence you need (instructions for use, oversight capabilities under Article 14, logs, registration), the deployer controls under Article 26, the Article 26(7) information plan per unit or entity, and whether Article 27 applies to you.
- Record and set triggers. Write the result as an AI Decision Record with the date, the reviewers, the alternatives considered and the triggers that re-open it: a new input feature, a new degree of delegation, a new unit or entity, a model version that changes the output, a contestation or new guidance.
Defaults. Re-check classification at least annually and within 30 days of any trigger. Treat any behavioural input to allocation as placing the function in point 4(b) until legal review concludes otherwise. Where the outcome is genuinely uncertain and the system affects many workers, classify as high-risk as a precaution; adapt this default to the organisation's risk appetite and to the works agreement or collective agreement.
Done when each function of the system has a recorded classification, the prohibition check is evidenced, the role is stated, the consequences are mapped to named owners, and the workers' representatives have received the record.
Worked example: AIDR-0651 and FRIA-2026-007
The following examples are illustrative. Hansa Mutual's claims-triage agent was classified as not high-risk in AIDR-0024 for its insurance function of routing claims. That classification remains correct for that purpose, but the agent also allocates claims to individual claims handlers and produces throughput figures per handler that team leaders see under the group works agreement KBV-IT-2024. AIDR-0651 reassesses that second purpose. The review found that the allocation rules weighted each handler's open workload, skill tags and a capacity factor derived from the handler's throughput over the previous four weeks, a behavioural input in the sense of the draft guidelines.
# decisions/AIDR-0651.yaml (illustrative)
id: AIDR-0651
title: Claims-triage agent, work-allocation function, AI Act classification
date: 2026-12-14
status: accepted
reopens: AIDR-0024   # insurance routing function; that classification stands
system: claims-triage agent
usage_mode: Mode 5 Autonomous production agents
role: provider and deployer
function_assessed: allocation of claims to individual claims handlers
management_functions: [M1 Direction, M2 Evaluation]
delegation:
  M1 Direction: Level 3 Bounded   # within allocation rules; team leader may reassign
  M2 Evaluation: Level 1 Assisted
findings:
  prohibition_check: no inference of emotions; no biometric input
  annex_iii_4b:
    task_allocation_on_behaviour: true   # throughput-based capacity factor
    monitoring_and_evaluation: true      # per-handler figures to team leaders
  article_6_3_available: false           # evaluates individual performance: profiling
decision: >
  Treat the work-allocation function as high-risk under Annex III point 4(b).
  Remove the throughput-based capacity factor from allocation from release 7.0;
  allocate on skill tags, open workload and declared availability only.
  Keep per-handler figures for team leaders only, as KBV-IT-2024 provides.
alternatives_considered:
  - Rely on Article 111(2) for a system already in service: rejected; allocation rules change monthly
  - Remove per-handler figures to leave point 4(b): rejected; team leaders need them for workload balance
applies_in: [DE, NL, SE, PL, NO, UK, CH]   # law in EU entities, group policy elsewhere
obligations: [Articles 9 to 15, Article 17, Annex VI, Article 49(1), Article 26]
deciders: [group AI governance board, chief HR officer]
consulted: [Konzernbetriebsrat, group data protection officer]
reopen_on: [new allocation input, change of degree of delegation, new entity, contestation]
Nordvik Region is a body governed by public law, so before ShiftWise goes live in home care it must complete a fundamental rights impact assessment under Article 27. ShiftWise falls under point 4(b) because the rosters and visit schedules it drafts set working hours, rest and the pace of visits, and unit managers rely significantly on them when they approve. The excerpt below shows the home-care section of FRIA-2026-007; the hospital section has the same structure.
# assessments/FRIA-2026-007.yaml (illustrative excerpt, home-care section)
id: FRIA-2026-007
system: ShiftWise
provider: supplier under tender NR-2025-089
deployer: Nordvik Region
classification: high-risk, Annex III point 4(b); see AIDR-0602
owner: Ingrid Halvorsen, HR director
reviewers: [AI governance lead, data protection officer, chair of the central work-environment committee]
dpia_cross_reference: DPIA for ShiftWise, sections 3 to 5   # Article 27(4) as amended
process: four-week rosters, daily visit schedules and routes, open-shift offers
period_and_frequency: rosters every four weeks; routes daily; open shifts continuously
affected_groups:
  - about 1,100 home-care staff, a high share part-time or hourly
  - residents receiving home care, through visit timing
risks:
  - id: R1
    right: fair and just working conditions, Charter Article 31
    harm: visit times too short for the care plan, raising pace and strain
  - id: R2
    right: non-discrimination, Charter Article 21
    harm: preferences of part-time staff weighted below full-time staff
  - id: R3
    right: data protection, Charter Article 8
    harm: behavioural data entering the optimiser through open-shift acceptance
oversight: unit managers approve every roster; may override with a recorded reason (DLG-NR-ROS-01)
measures_if_risks_materialise:
  - R1: safety representative may require review of planned visit times
  - R2: quarterly comparison of preference fulfilment by contract type
  - R3: open-shift offers go to all opted-in staff; ranking prohibited
complaints: contestation records CNT-NR-*, answered within 10 working days
information_article_26_7: unions informed and negotiation held before go-live (AIDR-0602)
notified_to_market_surveillance_authority: true
review: on any change to optimisation objectives or offer rules; at least annually
Across the usage modes
The Act classifies by intended purpose, not by mode. The mode still matters, because it determines who is provider, where the evidence sits and how easily a management function arrives unannounced.
| Usage mode | How a management function appears | AI Act consequence |
|---|---|---|
| Mode 0 Ambient AI | Productivity, collaboration or wellbeing analytics in licensed suites | Can be high-risk under point 4(b) or prohibited under Article 5(1)(f); arrives with a licence update, so the prohibition check runs on every release |
| Mode 1 Conversational assistants | A manager asks an assistant to rank applicants or rate a team | The manager's use defines the purpose; policy forbids point 4 uses in general assistants |
| Mode 2 Embedded workplace assistants | Task lists with named owners, meeting summaries that attribute actions | Usually outside point 4 while advisory; inside once outputs feed evaluation of individuals |
| Mode 3 Agentic work tools | Agents that assign tickets or review colleagues' output | Point 4(b) if allocation uses behavioural inputs; the deployer may become provider by changing the purpose |
| Mode 4 Built AI applications | Rostering, screening, scoring and dashboards | Classic point 4 systems; employer is deployer when it buys and provider when it builds |
| Mode 5 Autonomous production agents | An agent that allocates work to people at Level 3 Bounded | Point 4(b) whatever its architecture; Level 4 Autonomous never used for M3 Consequence |
The degree of delegation does not change the classification either. The draft guidelines treat a decision formally taken by a person who relies significantly on the output as a decision in the sense of point 4(b), so Level 1 Assisted and Level 2 Supervised do not move a system out of scope. They change what Article 26(2) and Article 86 require: at low degrees the record must show what the person added, and at high degrees the evidence sits in the delegation profile a named person approved, as AI Red Team, Chapter 6 concluded for the autonomy levels (43, Nordqvist, 2026).
Nordvik Region and Hansa Mutual
Nordvik Region deploys ShiftWise, procured under tender NR-2025-089, as a high-risk system under Annex III point 4(b). As a public authority it will register its use in the EU database under Article 49(3), which is expected with the Annex III obligations from 2 December 2027, and it checks that the supplier has registered the system, completes FRIA-2026-007 with the DPIA cross-referenced and notifies the market surveillance authority. Before go-live in home care it informs the unions and negotiates under its co-determination act, recorded in AIDR-0602, and Mikael Strand's Strandvik unit receives the worker information notice before its first roster. Unit managers are the overseers under Article 26(2), trained under Article 4 and holding written authority to override any roster with a recorded reason; the Region does not rely on the transitional rule. For the home-care dashboards, which the profile left open, the Region applied the practical guide in AIDR-0609. The dashboards show individual planned-against-actual figures to the unit manager, which is monitoring and evaluation of individual performance and therefore profiling, so the derogation is unavailable. The Region decided, as a precaution, to treat them as high-risk under point 4(b). Because it built them in house, it is their provider as well as their deployer, which brings Articles 9 to 15, Annex VI and registration under Article 49(1) to a small digitalisation unit; the condition from Chapter 8, that individual figures may not be used in pay reviews or disciplinary matters, stays in DLG-NR-HCD-01. This is Q10 in practice: a public employer can hold itself to legality only for systems whose evidence it controls, through the tender for what it buys and its own repository for what it builds, as AI Governance, Chapter 17 concluded (41, Nordqvist, 2026).
Hansa Mutual reopened the classification of the claims-triage agent's work-allocation function in AIDR-0651 and treats it as high-risk; as the agent's builder it carries the provider's obligations and generates the Annex IV documentation from its architecture repository, as AI Platform and Security, Chapter 5 recommended (42, Nordqvist, 2026). It keeps TalentLens as high-risk under point 4(a) as a deployer, with the supplier's affect and voice analysis switched off group-wide under Article 5(1)(f), and verifies after each supplier release that no inferred-emotion field appears in interview transcripts or exports; candidates are told under Article 26(11) that the system is used. No rights impact assessment is required of Hansa for these systems; it assesses them within its DPIAs. Its harder problem is geography: the AI Act is law in the German, Dutch, Swedish and Polish entities, applies in Norway only once incorporated into the EEA Agreement and does not apply in the United Kingdom or Switzerland. In AIDR-0657 the group applies one baseline of AI Act controls for management systems to all seven markets as group policy, records in each market overlay whether a control is law or policy, and runs the Article 26(7) information step through each entity's own body, from the Konzernbetriebsrat in Germany to the employee committee in Switzerland. Thomas Brandt received AIDR-0651 before the board accepted it. The difference between the organisations is that Nordvik's duties fall mainly on what it buys, as a public deployer, while Hansa's fall on what it builds, as a provider.
Summary
The AI Act treats the AI boss as high-risk. Annex III point 4(a) covers recruitment and selection; point 4(b) covers decisions affecting the terms of work, promotion and termination, task allocation based on individual behaviour or traits, and the monitoring and evaluation of performance and behaviour. Read against the five management functions, the listing covers M1 Direction where allocation uses behavioural inputs, M2 Evaluation wherever individuals are monitored or rated, and M3 Consequence throughout, while M5 Care is protected by the prohibition of emotion recognition at the workplace in Article 5(1)(f) and the duty to inform workers' representatives and affected workers in Article 26(7). The derogation in Article 6(3) rarely helps a management system, because evaluating individual workers is profiling, and profiling closes it.
The deployer's duties turn the named human decider into law: competent oversight with authority, monitoring, logs, prior information to workers, an impact assessment for public bodies and an explanation under Article 86. The Digital Omnibus deferred the high-risk obligations for Annex III systems to 2 December 2027, softened the wording of AI literacy without removing the oversight competence that Article 26(2) requires, and let deployers cross-refer between the rights assessment and the DPIA. The prohibition is observable law; the high-risk obligations are expected on a decided date; enforcement in employment is speculation.
The architectural response is to record classification per system and per function, evidence that prohibited features are off, name overseers with authority, inform before use and record each decision so that it can be explained. Nordvik does this as a public deployer and, for its dashboards, as a precautionary provider; Hansa does it as a provider across seven markets under one group policy.
Chapter 22 turns to the GDPR and the Platform Work Directive, which add the right not to be subject to a solely automated decision, meaningful information about the logic involved and, for platform work, the rule that decisions to restrict, suspend or terminate are taken by a human being.
Sources
- European Parliament and Council of the European Union (2024). Regulation (EU) 2024/1689 laying down harmonised rules on artificial intelligence (Artificial Intelligence Act). Official Journal of the European Union. (1, European Union, 2024)
- European Parliament and Council of the European Union (2026). Regulation (EU) 2026/1744 amending Regulations (EU) 2024/1689, (EU) 2018/1139 and (EU) 2023/1230 as regards the simplification of the implementation of harmonised rules on artificial intelligence (Digital Omnibus on AI). Official Journal of the European Union. (2, European Union, 2026)
- European Commission (2026). Draft Commission guidelines on the classification of high-risk AI systems. Shaping Europe's digital future. (3, European Commission, 2026)
- European Commission (2025). Commission Guidelines on prohibited artificial intelligence practices established by Regulation (EU) 2024/1689 (AI Act). (58, European Commission, 2025)
- European Commission (2026). AI literacy: questions and answers. Shaping Europe's digital future. (4, European Commission, 2026)
- European Parliament and Council of the European Union (2016). Regulation (EU) 2016/679 (General Data Protection Regulation). Official Journal of the European Union. (5, European Union, 2016)
- European Parliament and Council of the European Union (2002). Directive 2002/14/EC establishing a general framework for informing and consulting employees in the European Community. Official Journal of the European Communities. (51, European Union, 2002)
- Federal Republic of Germany (2001). Betriebsverfassungsgesetz (BetrVG). (9, Germany, 2001)
- Sveriges riksdag (1976). Lag (1976:580) om medbestämmande i arbetslivet. (205, Sveriges riksdag, 1976)
- European Union (2012). Charter of Fundamental Rights of the European Union. Official Journal of the European Union. (48, European Union, 2012)
- European Parliament and Council of the European Union (2024). Directive (EU) 2024/2831 on improving working conditions in platform work. Official Journal of the European Union. (47, European Union, 2024)
- International Organization for Standardization and International Electrotechnical Commission (2023). ISO/IEC 42001:2023 Information technology — Artificial intelligence — Management system. ISO. (10, ISO/IEC, 2023)
- Council of Europe (2024). Framework Convention on Artificial Intelligence and Human Rights, Democracy and the Rule of Law (CETS No. 225). (59, Council of Europe, 2024)
- Nordqvist, G. (2026). AI Governance: Governing Artificial Intelligence in European Enterprises and Public Authorities. (41, Nordqvist, 2026)
- Nordqvist, G. (2026). AI Platform and Security: Building and Securing AI Platforms in European Enterprises and Public Authorities. (42, Nordqvist, 2026)
- Nordqvist, G. (2026). AI Red Team: AI as an Active Part of Cyber Defence in European Enterprises and Public Authorities. (43, Nordqvist, 2026)
- Nordqvist, G. (2026). The Transformed Security Architect: Role, Craft and Career in the Age of AI in European Enterprises and Public Authorities. (46, Nordqvist, 2026)